[ Package conformance ]
Auth & Payments · >=12.0.0
expo-secure-store
upstream expo-secure-store JS runs unchanged; package-local wrapper only registers the ExpoSecureStore native module backed by tenant-scoped IndexedDB records encrypted with AES-GCM via WebCrypto. Bun/test environments without IndexedDB use the same encrypted record format in memory. (same golden-rule native-seam tier as expo-crypto / expo-network: upstream JS runs unmodified, every gap is a physically-absent-on-an-iOS-sim feature.)95%
API coverage
← iOS 26.4|Peach →
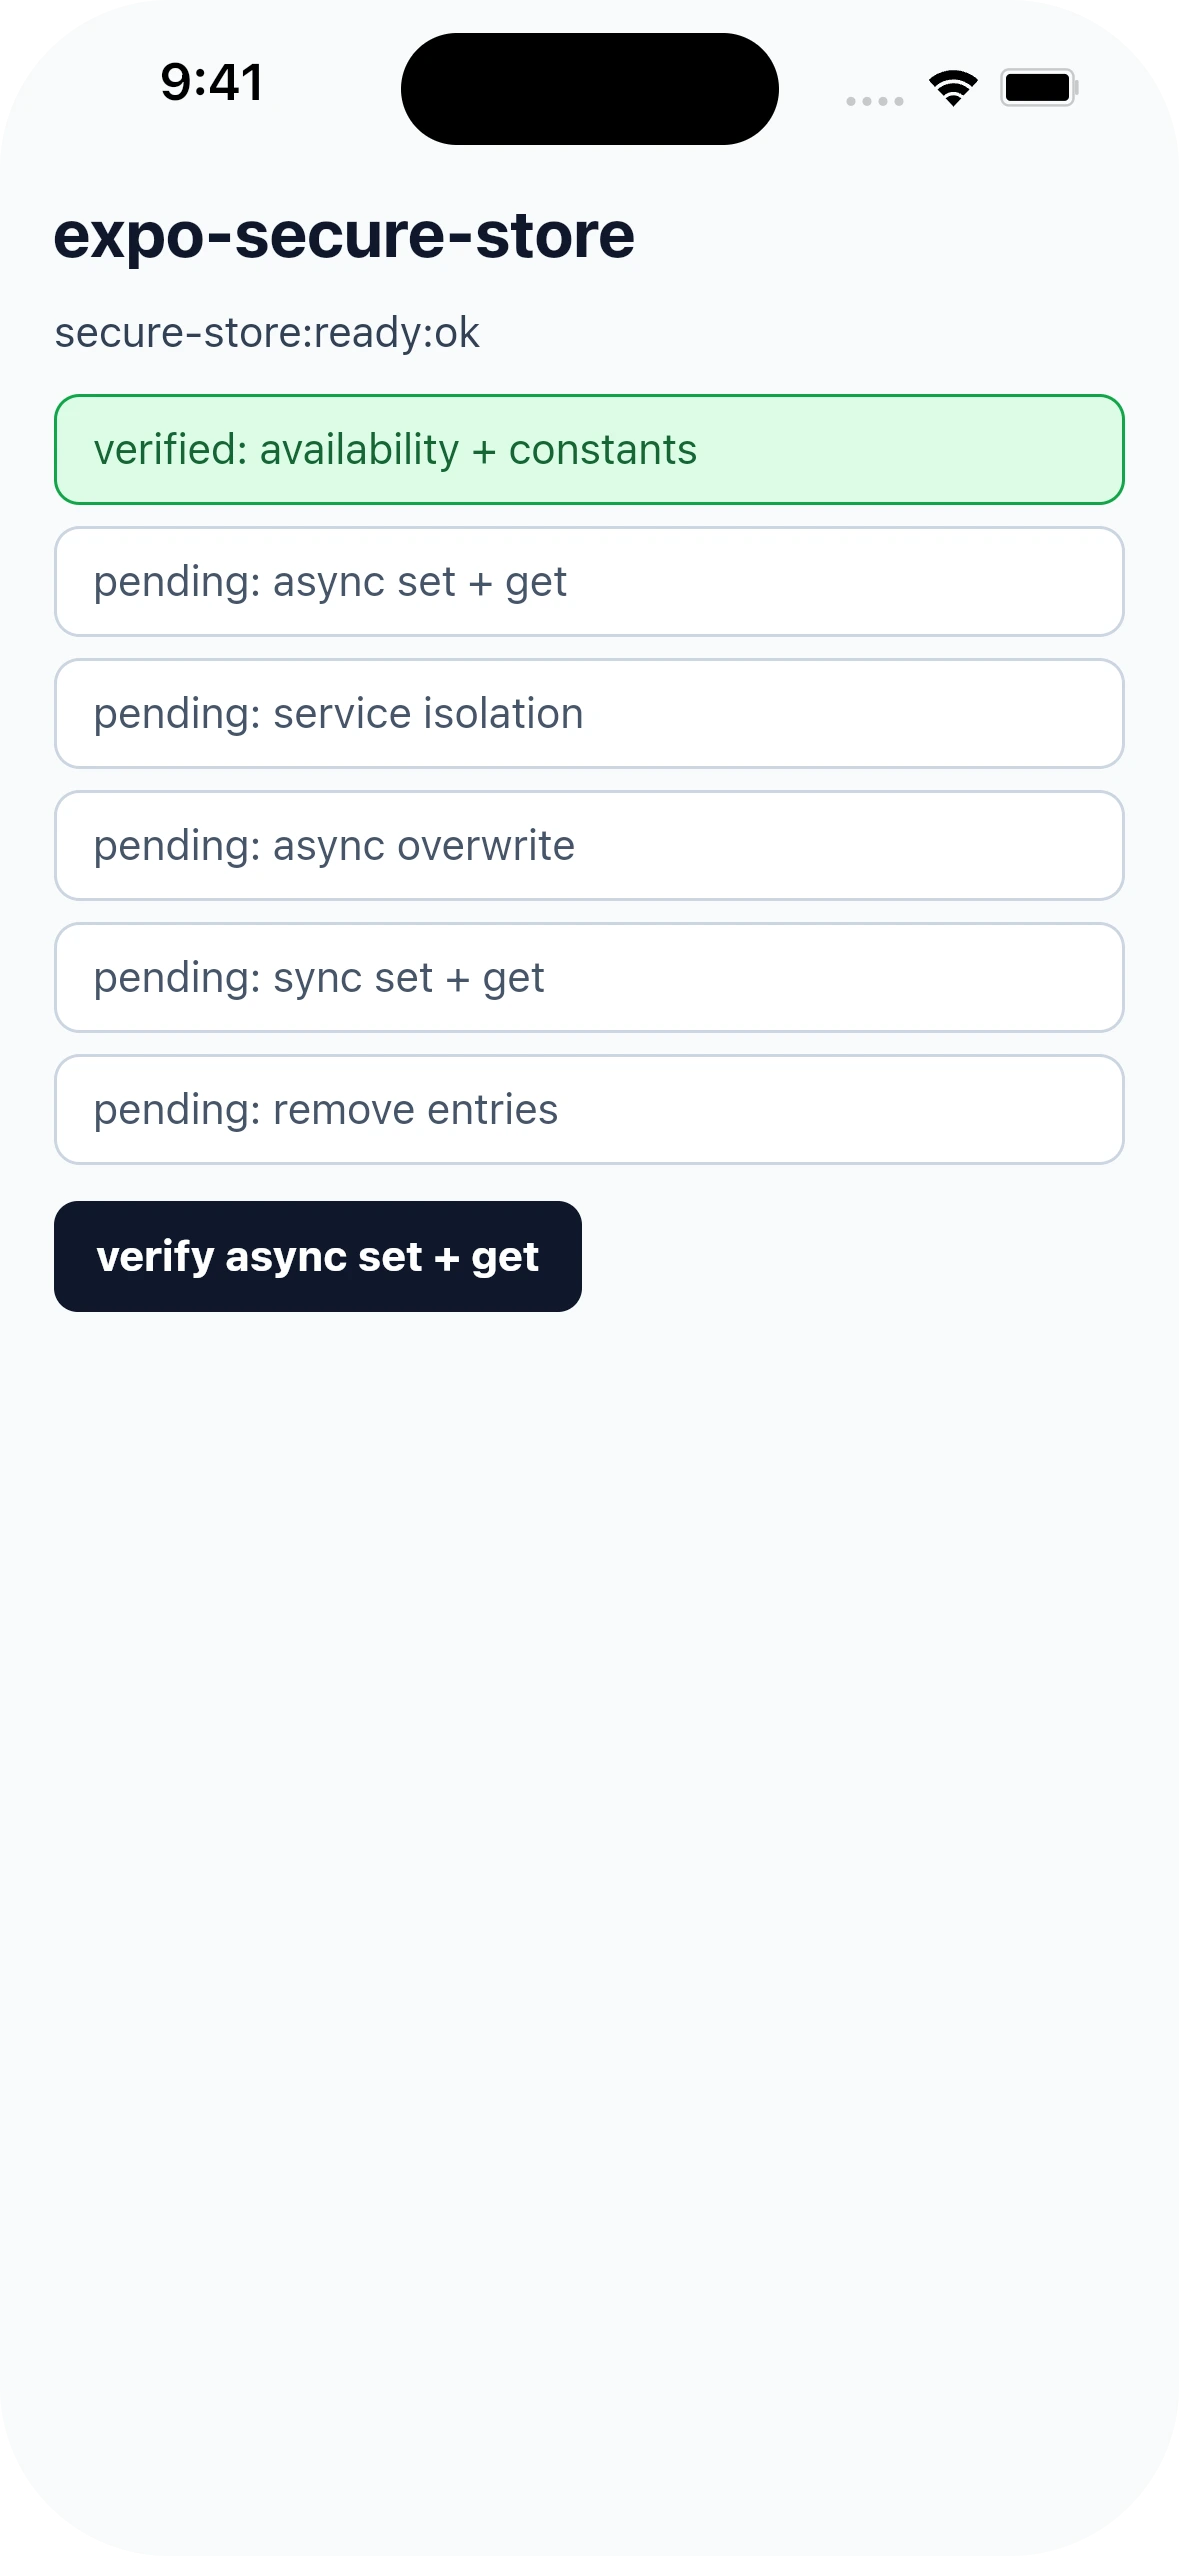
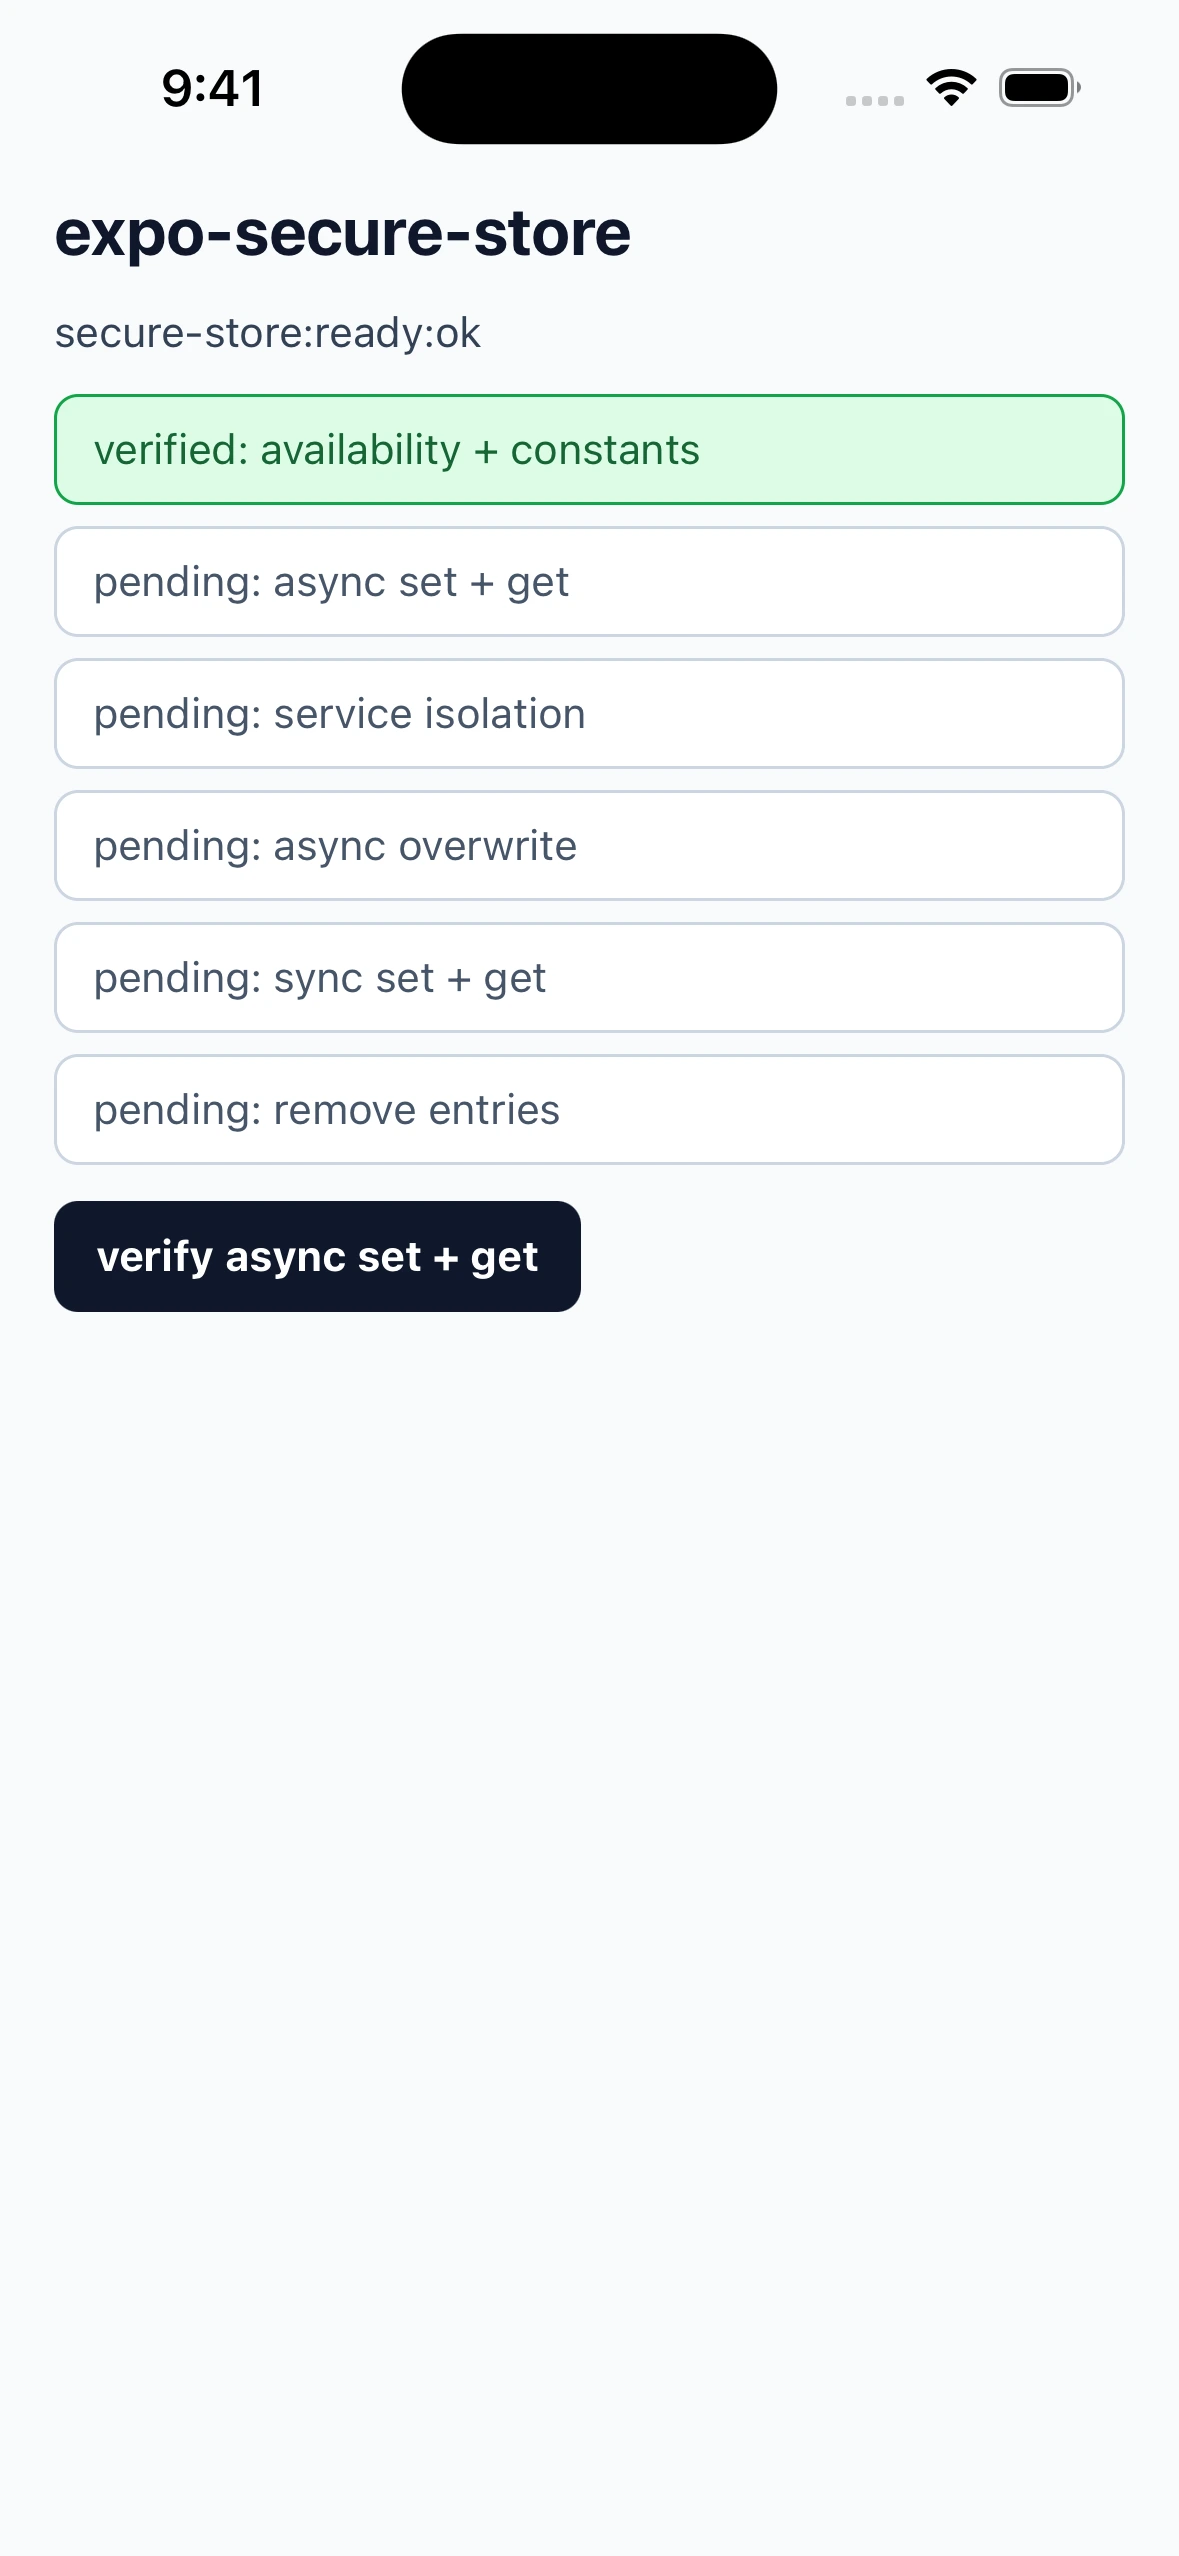
secure-storeExpo Secure Storeexpo-secure-store dense storage lifecycle. Proves availability and constants, async storage and overwrite, keychain-service isolation, sync storage, and removal in six visual checkpoints.
Diff0.19%
DeviceiPhone 16
OracleiOS 26.4
CapturedAug 20, 2026
iOS 26.4PeachDiff
Expo Secure StoreiOS 26.4
Expo Secure StoreiOS 26.4
Expo Secure StoreiOS 26.4
Expo Secure StoreiOS 26.4
Expo Secure StoreiOS 26.4
Expo Secure StoreiOS 26.4
Working (8)
upstream validation and constantsgetItem/setItem sync APIs over the hydrated in-process cachegetItemAsync/setItemAsync/deleteItemAsync async APIsisAvailableAsynccanUseBiometricAuthentication falsekeychainService/accessGroup/requireAuthentication storage partitioningAES-GCM encrypted storage records with per-record salt/iv and tenant-scoped PBKDF2 key derivationpersists across reloads when IndexedDB is available
Missing (3)
canUseBiometricAuthentication always false (no biometric prompt available on web — correct unavailable shape)requireAuthentication not enforced beyond storage partitioning/encryption (no biometric prompt to require)keychainAccessible does not affect browser storage access. sync reads cannot synchronously cold-load IndexedDB after a fresh worker boot; async reads hydrate the cache. all of these are honest absent-on-web semantics — apps with graceful-degradation paths behave correctly.